Run the service desk. Keep the record.
FrexCore is one place for every request, every asset and every change. Tickets that get owned and answered against a target. An estate register that says who has what, what it cost and when the warranty runs out. Change control that stops the outages you cause yourself.
The audit trail comes out of doing the work, rather than being a second job somebody does the week before the assessor arrives.
Running today for clients across Africa, the United Kingdom, Australia and Papua New Guinea.
What your team works in every day.
Screens from a running system. Not mockups, not a staged tenant with four tickets in it: a working desk with a year of history behind it.
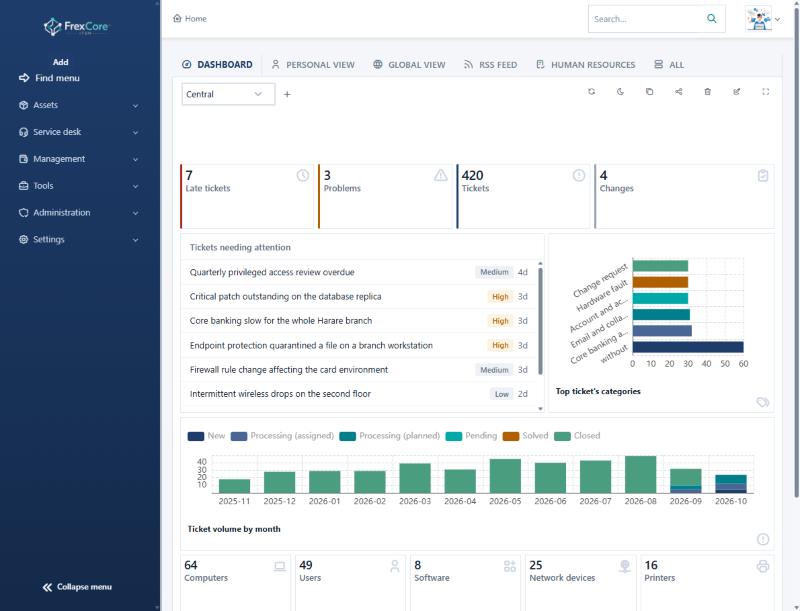
It opens on what is late, not on how many laptops you own. Seven tickets past their target, three open problems, four changes in flight: the things that need a decision this morning, before the counts that do not.
The attention list runs oldest first. Newest first shows the work that has been waiting least, which is the opposite of useful on a morning when the desk is behind.
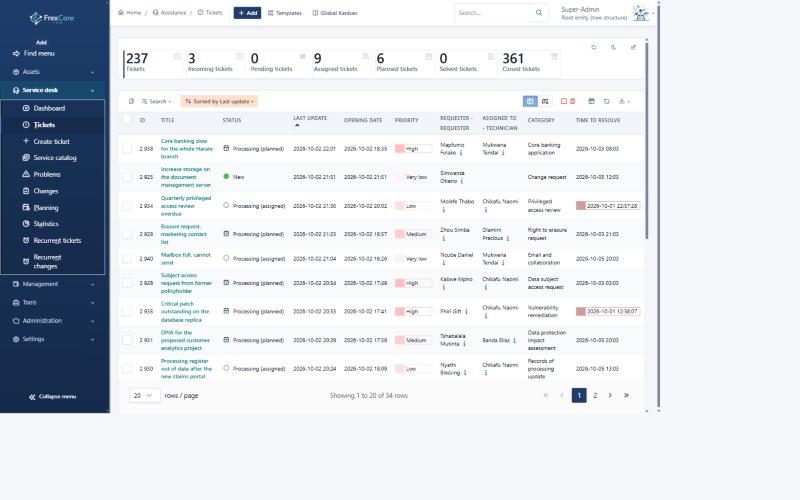
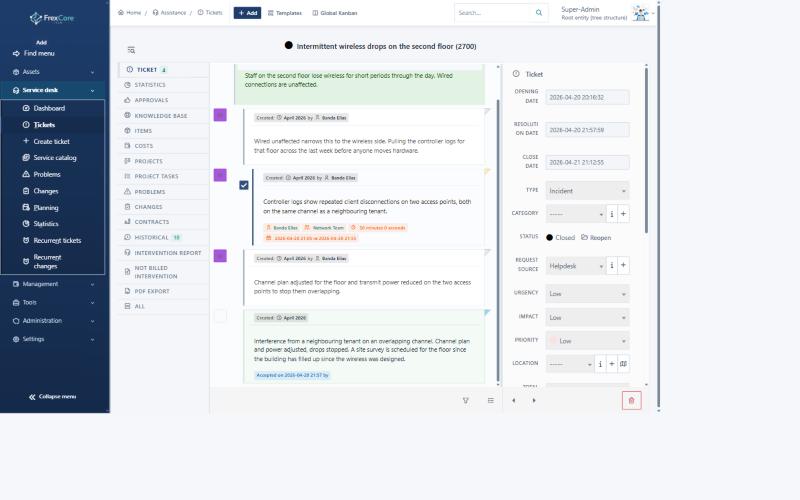
Service management, asset management, change control.
Three disciplines most organisations run in a shared mailbox, a spreadsheet and somebody’s memory. That works until the person leaves, the mailbox hits its quota, or somebody asks what happened in March.
Service desk and request management
Requests arrive by email, portal or phone and land in one queue with an owner, a category and a clock. Nothing waits on someone remembering it.
- Email becomes a ticket, replies stay on the thread
- Assigned to a team as well as a person, so leave does not stall work
- Resolution targets by priority, with what is late visible before a customer says so
Asset and configuration management
Every machine, licence, contract and supplier with an owner against it. The answer to “what do we actually have” stops being a stocktake.
- Hardware with who holds it, what it cost and when the warranty ends
- Software seats counted against what you bought, so renewals are a decision
- Contracts and suppliers with notice periods that surface before they lapse
Change and problem management
Most outages are self-inflicted. Changes get approved before the window and evidenced after it, and faults that keep coming back get treated as one thing.
- Approval, window and backout plan recorded before anything moves
- Evidence captured after, which is what an assessor asks to see
- Recurring faults raised as a problem instead of closed again each month
Isolation by design, not by query.
Everything above is the operational product, and our competitors have a version of it. This is the part they do not. Each client runs as a separately credentialed instance behind a filtering edge and a closed perimeter, so separation is enforced by the operating system rather than by a condition in application code.
Separation enforced below the application
Your records sit in a database only your instance holds credentials for, written by a process running under an account only your instance owns.
Recovery scoped to one client
Backups are per instance and encrypted off site, with a defined retention period and restores exercised rather than assumed.
Release control on your calendar
Each instance carries its own application tree, and a release is installed only after it matches a recorded hash.
Three people have to be satisfied.
A service management platform gets bought by one of them, used by another and assessed by the third. It fails if it only serves one.
The executive
A fixed cost per person with no module to discover later. Visibility of what the estate is worth and what it is costing. Reporting that can go into a board pack without someone spending a weekend assembling it.
The IT manager
Work that cannot fall through: an owner and a target on every request, a queue that survives leave and turnover, and a position on service performance that is measured rather than argued.
The security and compliance lead
Demonstrable separation, access review, change control and an audit trail produced by the work itself. Evidence available on the day it is asked for, rather than reconstructed the week the assessor arrives.
When the regulator asks, you already have the record.
You are not buying this for the compliance. You are buying it to run the desk. But the desk is where the evidence lives, so a system that captures the work properly answers the assessor as a by-product.
FrexCore categorises work by the obligation behind it, so a subject access request arrives with a statutory clock attached rather than as a ticket called “query”. The register is configured per instance, so a client in Manchester and a client in Port Moresby each see the obligations that apply to them.
The full jurisdiction register- Europe and the United Kingdom
- UK GDPR and the Data Protection Act 2018 as amended by the Data (Use and Access) Act 2025, and GDPR Articles 28 and 33.
- Asia-Pacific
- The Privacy Act 1988 with the Australian Privacy Principles and the Notifiable Data Breaches scheme, and Papua New Guinea’s Digital Government Act with a comprehensive bill in consultation.
- Africa
- POPIA, Zimbabwe’s Cyber and Data Protection Act, Kenya’s Data Protection Act 2019, Nigeria’s NDPA 2023 and Botswana’s Data Protection Act.
- Certification frameworks
- ISO 27001 Annex A and PCI DSS: change control, access reviews, asset ownership and incident records in the form an assessor asks for.
Priced per person, not per promise.
No setup fee, no minimum seat count, no module you discover you needed in month three. Pay annually and take 15 percent off. Prices in US dollars.
- Service desk and self-service portal
- Asset and licence register
- Knowledge base and service level targets
- Isolated instance with daily backup
- Everything in Essential
- Change and problem management
- Contract and supplier register
- Custom dashboards and API access
- Everything in Professional
- Multiple entities and branches
- Single sign-on
- Data processing agreement and compliance pack
Who is behind it.
FrexCore is built by Frexwell Technologies. We advise on governance, risk and compliance for financial services, mining and the public sector, and we built FrexCore because the tooling our clients could afford did not hold up to the standards we were asking them to meet.
That practice now runs across three continents, which is why the product treats a second jurisdiction as configuration rather than as a special case.
- Founded and led by a CISSP and Certified Ethical Hacker (Master), with an MSc in Artificial Intelligence.
- Contributed as a subject matter expert to Zimbabwe’s Cyber and Data Protection Act and its amendment process.
- Helped develop the Data Protection Officer curriculum and training materials used in Zimbabwe.
- Operational technology and SCADA security work across mining and power utilities.
- Background in IT audit and cybersecurity at a Big Four firm, advising across Africa, Europe and the Pacific.
See it with your own data in it.
Forty minutes on your real situation: what you are running now, where work goes missing, and what a migration would involve. The architecture and control summary goes out beforehand, so your security people arrive having read it. If it is not a fit we will say so on the call.
Book a walkthrough- [email protected]
- Call or message
- +61 480 010 143
- Hours
- We answer across African, European and Pacific time zones.